Session tokens
Keyward keeps two things for a signed-in user: a long-lived session, and a short-lived session token your API verifies on every request.
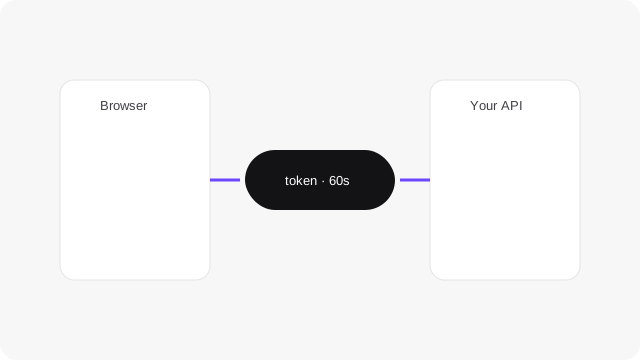
The token lives for 60 seconds and is refreshed in the background, so a revoked session stops working within a minute without a database lookup per request.
Claims
Claim | Meaning |
|---|---|
| The user ID |
| The session ID |
| The active team, if any |
| Expiry, 60 seconds after issue |
Updated
What did you think of this content?