Reproducing, disclosing and fixing an image-decoder vulnerability with the maintainers

In August, an independent researcher reported what looked like a remote code execution vulnerability in our image optimization. The bug was not in our code. It was three dependencies down, in a decoder for a modern image format.
The dependency chain
Image optimization lets applications resize images on the fly. For one format, the chain looked like this:
The router hands
/_imgrequests to the optimizerThe optimizer calls a native resize library
The resize library calls a format decoder
The decoder parses untrusted bytes
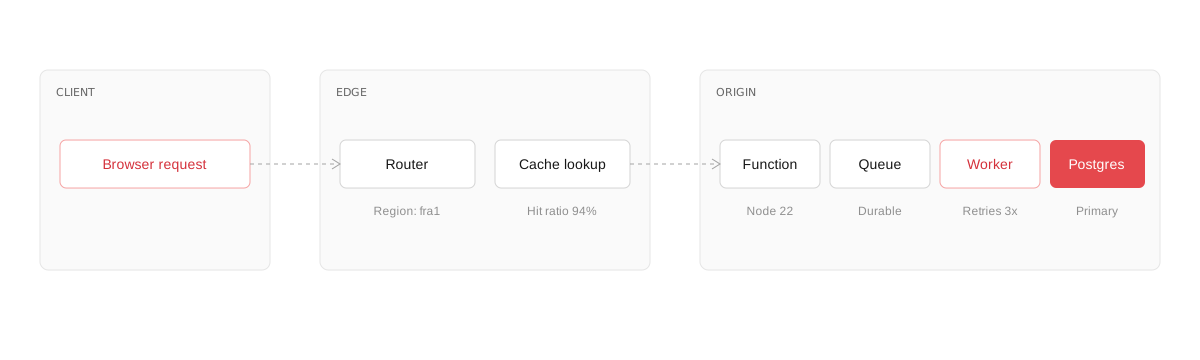
That meant the vulnerable code was not ours, but it was reachable through us.
Disclosure timeline
August 11–12: The researcher reported the issue; we reproduced it
August 13: We shipped a platform mitigation disabling that format
August 19: We met the decoder maintainers and agreed on a fix
August 25: A patched decoder release shipped upstream
 export default {
-  formats: ['avif', 'webp', 'jpeg'],
+  formats: ['webp', 'jpeg'],
   sizes: [640, 1080, 1920],
 }
Credit
Thanks to the researcher for a careful report, and to the maintainers who turned a fix around in under two weeks.